TL;DR
A group-wide compliance mandate, met by three people. What mattered was not how few they were but how the mandate traveled: down into each business unit and back up in one voice. It was met on time, and the working group outlived it.
The situation as found
When the General Data Protection Regulation (GDPR) entered into force, every company in the group’s orbit joined one working group, through the project lead each entity designated. Mine was a company of about two hundred people: many business units, central functions, and mutualized audience and IT services, far from ready, and held by its CAC40 parent to reinforced obligations.
What made it hard was its reach:
- A working surface of at least thirty direct interlocutors.
- Services not sized to absorb that kind of demand.
- A fixed legal deadline.
- Three people to carry it.
I was tapped as project manager backing the future data protection officer (DPO), a legal manager already acting as the information-and-liberties correspondent. A mandate wider than its team is exactly what vision to execution exists to answer.
The diagnosis
Most operators read the situation as a staffing problem: a legal deadline and three people. I read it as a mechanism problem. Nothing carried a mandate held at the top of the group into each business unit’s running work, or carried what the field reported back up in one voice.
The bottleneck was reach and translation, not the volume of compliance work.
What was decided, and why
The reflex answer was to widen the team to cover the stakeholder surface. That was never the shape of the problem, so I made the small team smarter instead.
I asked for one more person: a senior Scrum Master who already knew every business unit and its systems. I ran the rollout agile, adapting Scrum to a compliance rollout instead of importing it whole. Each of the three mapped onto themes and stakeholders they already had contacts with.
This was a group of three, not me alone: the DPO and I backed each other.
What was actually built or changed
The rollout ran on a working mechanism, each piece answering a need:
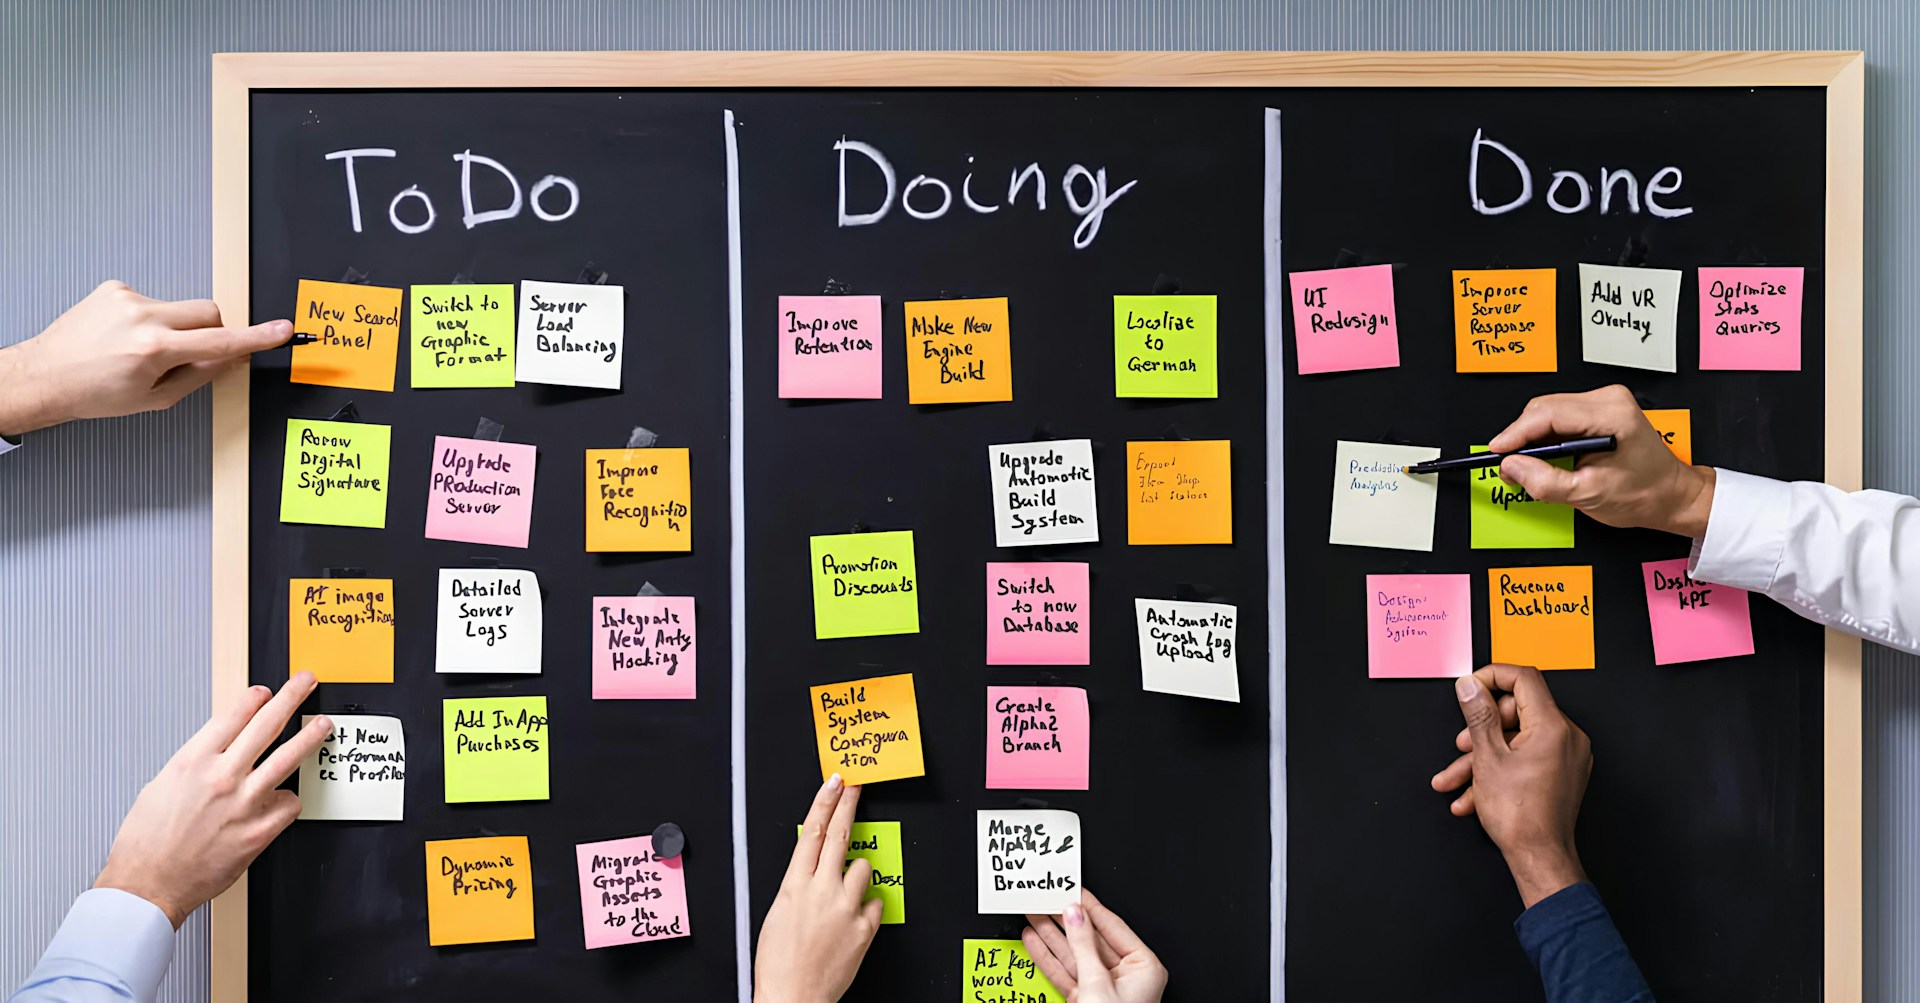
- An adapted Scrum rhythm. Sprints gave the rollout its cadence, keeping progress legible to management and the parent’s referents.
- Jira for traceability. Every theme was tracked in Jira, so any workstream’s state could be answered at any time.
- A thematic breakdown with relationship-mapped ownership. The DPO took HR and accounting, the Scrum Master the developers, and I, also running the web agency, marketing and commerce.
- Weekly meetings with an escalation route. Check-ins kept the trio unblocked; whatever was stuck went up to management.
- A two-step data flow. Any transverse subject first asked IT for an extract; the trio then shaped it and submitted it to the affected teams.
- The player-coach fill-in. Where the team ran out of people, I wrote the company’s complete information-systems security policy, never written before, in Confluence, interviewing the SysAdmin and the IT Director and having each part reviewed by its owner.
Through that rhythm the group stayed transparent to the control authorities. An IT audit across three domains applies the same discipline to a different compliance bar.
What broke, and what was got wrong
Two things did not go smoothly.
- The first was the human-resource gap: the security policy had never been written, and the trio had no capacity to write it. The fix was my doing it myself, because the team was under-resourced for a job nobody had done before.
- The second was the IT-data-extract bottleneck: every transverse theme depended on IT for its extract, forcing two-step working and slowing the themes that crossed business units.
The outcome, with its status
The implementation was delivered to the parent’s reinforced standard, on time, against the regulatory deadline. What it left behind lasted longer. The working group kept running agile, institutionalizing and reinforcing the company’s data-protection policy. The DPO received a budget for a legal assistant for the first two years. I was invited to take on the chief information security officer (CISO) role by default, offloading the IT Director and the SysAdmin from external relations and the partner-mandated audits while the DPO kept the authority relationship. The organization was praised for its efficiency and for offloading the other services’ mental load. Afterwards I was asked to run the group-wide cookie-consent platform.
The delivery, the institutionalized group, and the CISO role are the scope behind who I am. If this is the shape of your problem, let’s talk.